NEW YORK, Oct. 22 (TodayViralUSA) — Government agencies and businesses across Europe and Canada took websites offline this week after the disclosure of two critical flaws in PHP, the programming language that runs much of the web, as security firms warned that attackers were already moving to exploit them.
The PHP project released fixes on Wednesday in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. “If you run PHP, it is imperative that you update now,” the PHP Foundation said.
What the flaws do
The two vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, can each let an unauthenticated attacker run code on a server, and both carry a severity score of 9.2, according to the EU’s cybersecurity team, CERT-EU. They sit in memory management and error handling, parts of PHP that nearly every web request touches.
The PHP Foundation said that on servers using Apache with mod_php, a single unauthenticated request can trigger one of the flaws before any application code runs, and that full remote code execution was demonstrated with default settings. CERT-EU said proofs of concept had begun to circulate, raising the likelihood of active exploitation.
Sites pulled offline
The Dutch National Cyber Security Center took its own site down as a precaution, and organizations including the Port of Rotterdam and the government portal Overheid.nl followed, CNBC reported, citing Reuters. Finland’s state IT provider took government public network services offline, and France temporarily pulled local government administrative websites.
In Canada, some federal government websites were taken down temporarily, and the site for Elections B.C. was offline on the last day of advance voting, CBC News reported.
Cloudflare’s chief technology officer, Dane Knecht, said early attacks were emerging and the company was updating firewall rules, calling that “a STOPGAP only.”
What site owners should do
PHP runs roughly 75% of websites whose server language can be identified, according to the tracker W3Techs, and powers WordPress, which runs about 43% of all sites. The WordPress security firm Wordfence warned that WordPress’s automatic updates will not apply the fix and urged owners to find out who is responsible for updating PHP on their servers.
Agencies in Britain, Europe, Australia and Japan have advised operators to patch immediately or take internet-facing PHP services offline until they can. Security experts said small sites on shared hosting, where customers do not control the underlying servers, may stay exposed the longest.
Sources & Credits
- The PHP Foundation: Today’s PHP Security Release
- CERT-EU: Critical Vulnerabilities in PHP
- CNBC: Government websites go dark as software flaw sparks security scramble
- CBC News: Canadian government sites among those offline after PHP flaw
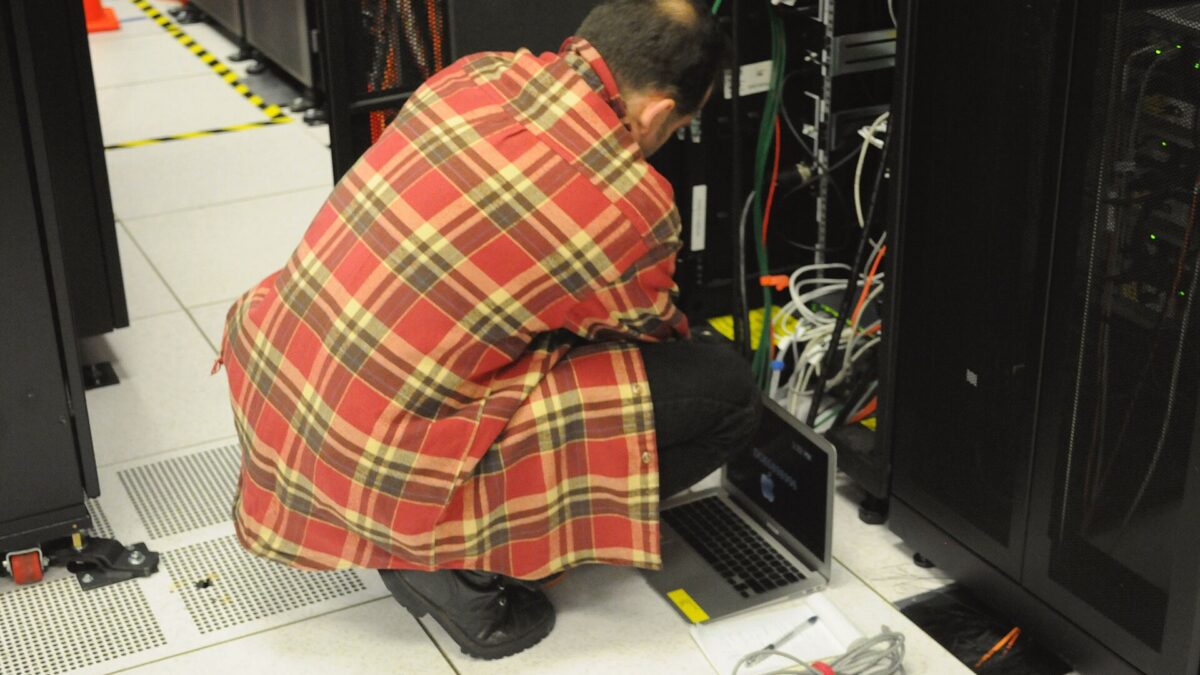
Image: Technician working on a server rack at NERSC (file photo), by Derrick Coetzee, CC0 1.0, via Wikimedia Commons.
Join the conversation