(TodayViralUSA) — Security researchers have documented a more capable and harder-to-detect version of DarkSword, a family of iPhone spyware, that can extract saved passwords, photos, Apple Notes and cryptocurrency-wallet data from compromised devices and take fresh orders from its operators every 15 seconds.
Mobile security firm iVerify said it found the variant, which it calls P7 DarkSword, while investigating an infection on a customer’s iPhone in August. The name comes from a “p7_” prefix the attackers used in their changes to the original DarkSword code. The company published its findings in an Oct. 8 report, and the research drew renewed attention this week.
Not a new iPhone flaw
P7 is not a new iOS vulnerability. It is a new version of the malware installed after a device has already been compromised through the DarkSword exploit chain, 9to5Mac reported. Earlier this year, Google and iVerify disclosed DarkSword, which affected iPhones running iOS 18.4 through iOS 18.7, prompting Apple to ship security updates, including iOS 18.7.7, for affected older versions of its software.
iVerify told 9to5Mac the infected device belonged to an employee of a financial institution, and that the group behind P7 is spreading it through malicious advertisements and compromised websites, so-called watering-hole attacks. That means victims may be caught up in broad campaigns rather than singled out. iVerify did not say which iOS version the infected phone was running.
What the variant can do
According to iVerify, P7 improves on earlier versions in three areas: it is stealthier, removing debug logging and reducing the number of times it injects itself into system processes; it is more stable, using browser storage to avoid re-infecting the same phone; and it is more capable.
Unlike earlier versions, which copied a phone’s entire keychain database for processing on the attackers’ servers, P7 extracts keychain data and packages it on the device itself before sending it out. It also adds dedicated routines for finding cryptocurrency-wallet apps and extracting wallet data.
The implant runs inside SpringBoard, the iOS process that manages the home screen, and checks in with the attackers’ command server every 15 seconds by default, an interval operators can change remotely. Through that two-way channel, attackers can order it to retrieve files, upload photos, list installed apps, copy Apple Notes databases, collect data from individual apps and scan the phone’s entire file system.
“P7 DarkSword shows that DarkSword operators are actively iterating on the implant,” iVerify wrote, adding that unlike many AI-assisted variants it has seen, “the P7 authors understood the code they were modifying.”
Leaked tools, wider reach
Apple told Fox News’ CyberGuy column that DarkSword originated as sophisticated, expensive mercenary spyware and that, after it leaked, the technology became available to ordinary criminals. Google said earlier this year that DarkSword had been used by multiple commercial surveillance vendors and suspected state-sponsored actors, with attacks seen in Saudi Arabia, Turkey, Malaysia and Ukraine, according to 9to5Mac.
How to protect a device
Because the exploit chain targets outdated software, the most effective defense is keeping iPhones updated to the latest version of iOS available for the device. iVerify’s report also lists network and on-device indicators that security teams can use to check for infection, and the firm noted that the new variant’s changes mean some earlier indicators of compromise no longer apply.
Sources & Credits
- iVerify: Sleep, Beacon, Steal, Repeat — The Story of P7 DarkSword Variant
- 9to5Mac: Researchers uncover new DarkSword spyware variant affecting unpatched iPhones
- Fox News: New iPhone spyware can steal passwords and photos
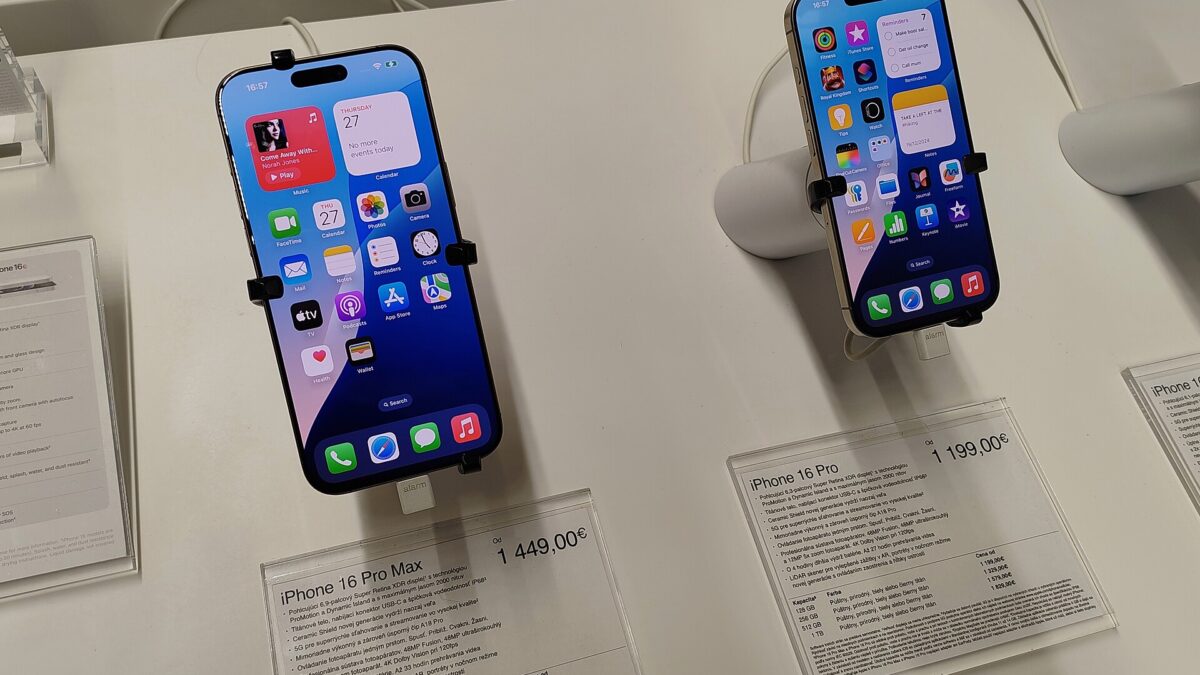
Image: iPhone 16 Pro and iPhone 16 Pro Max on display (file photo), by Jakub CA, CC BY 4.0, via Wikimedia Commons.
Join the conversation